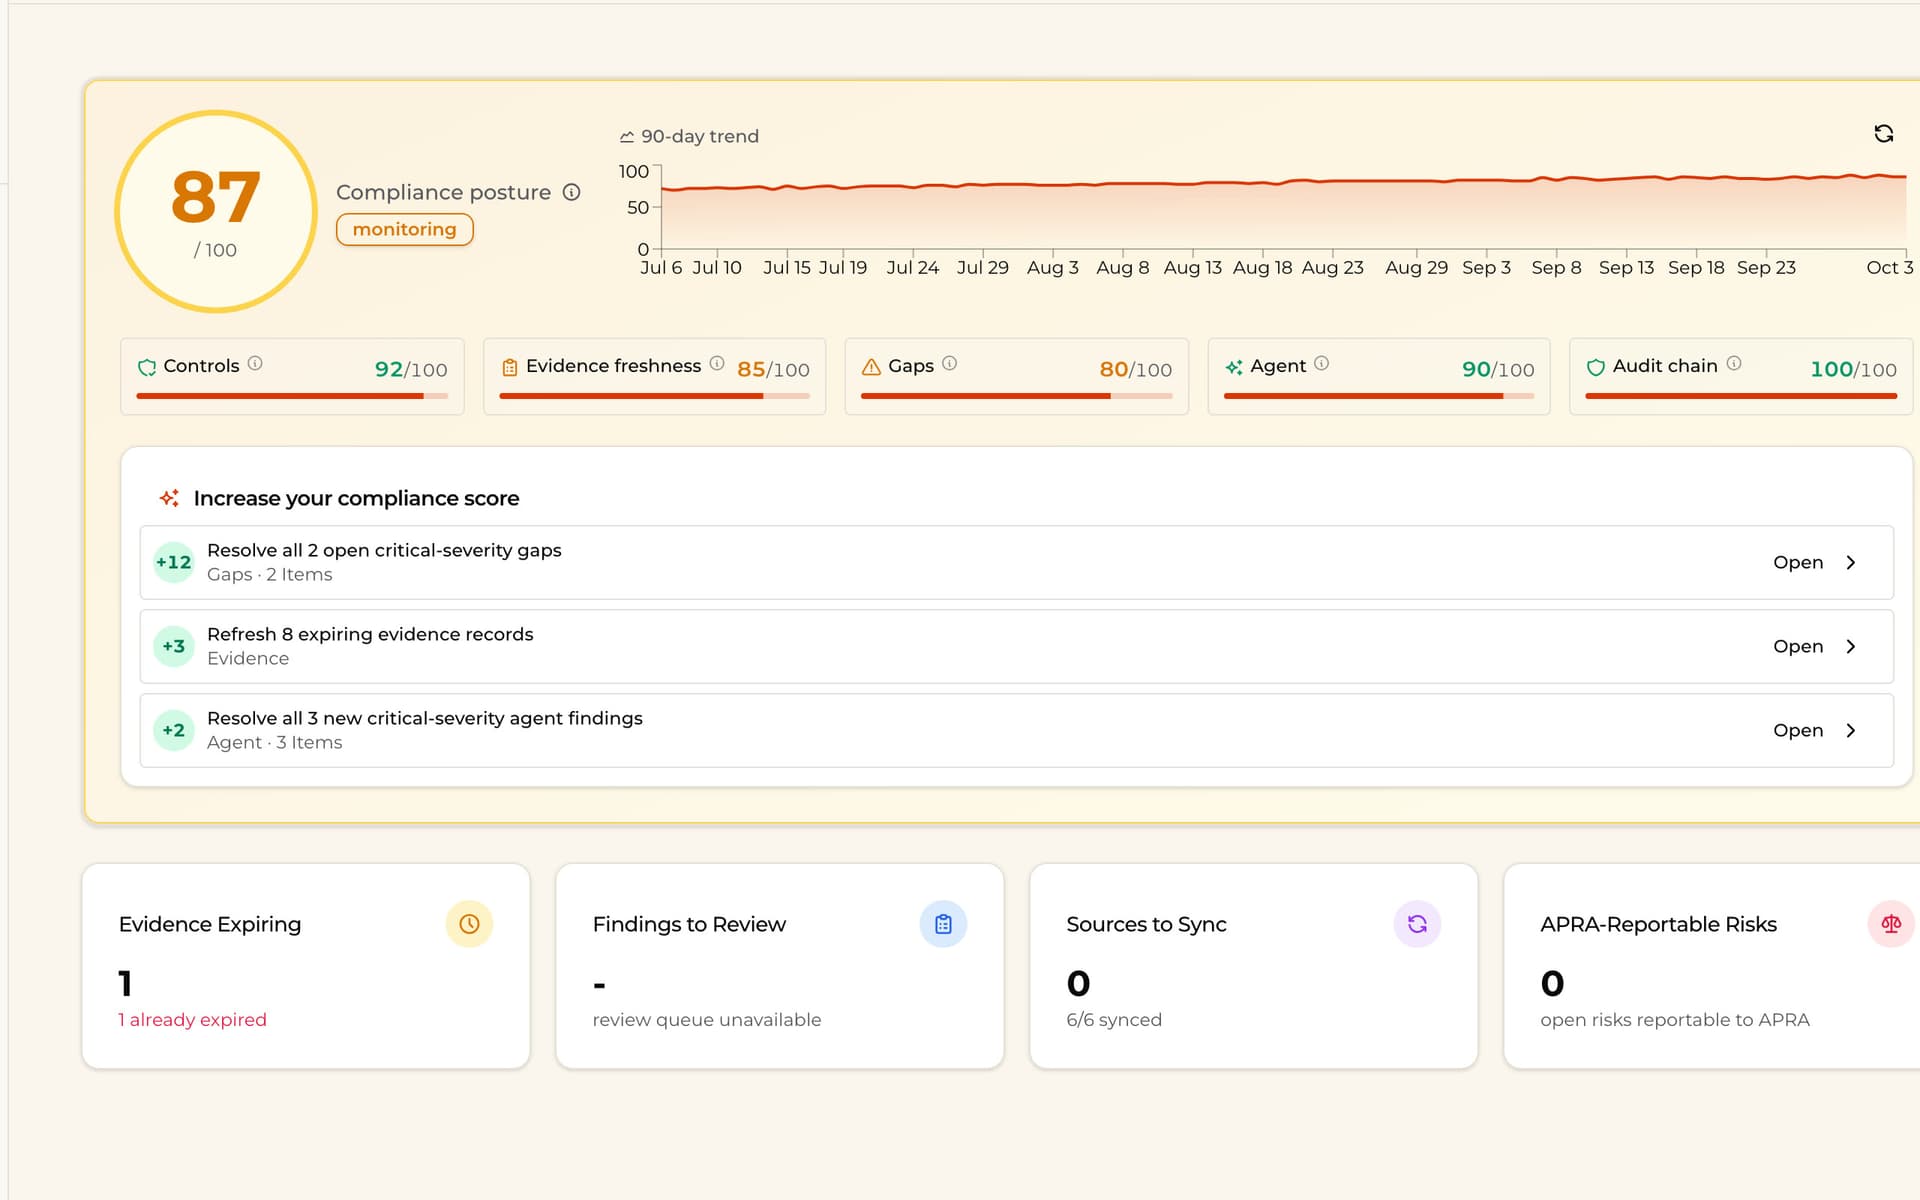
Evidence collected as you work. Not the week before the audit.
Every policy, test and attestation is registered against the controls and standards it proves, its expiry watched, so the audit pack already exists when you need it.
- every piece of evidence tied to its controls and frameworks
- Linkedevery piece of evidence tied to its controls and frameworks
- expiring evidence flagged before it lapses
- Watchedexpiring evidence flagged before it lapses
- a tamper-evident audit chain behind every change
- Recordeda tamper-evident audit chain behind every change
From scattered files to a standing audit pack. Three steps.
- 01
Register the evidence once
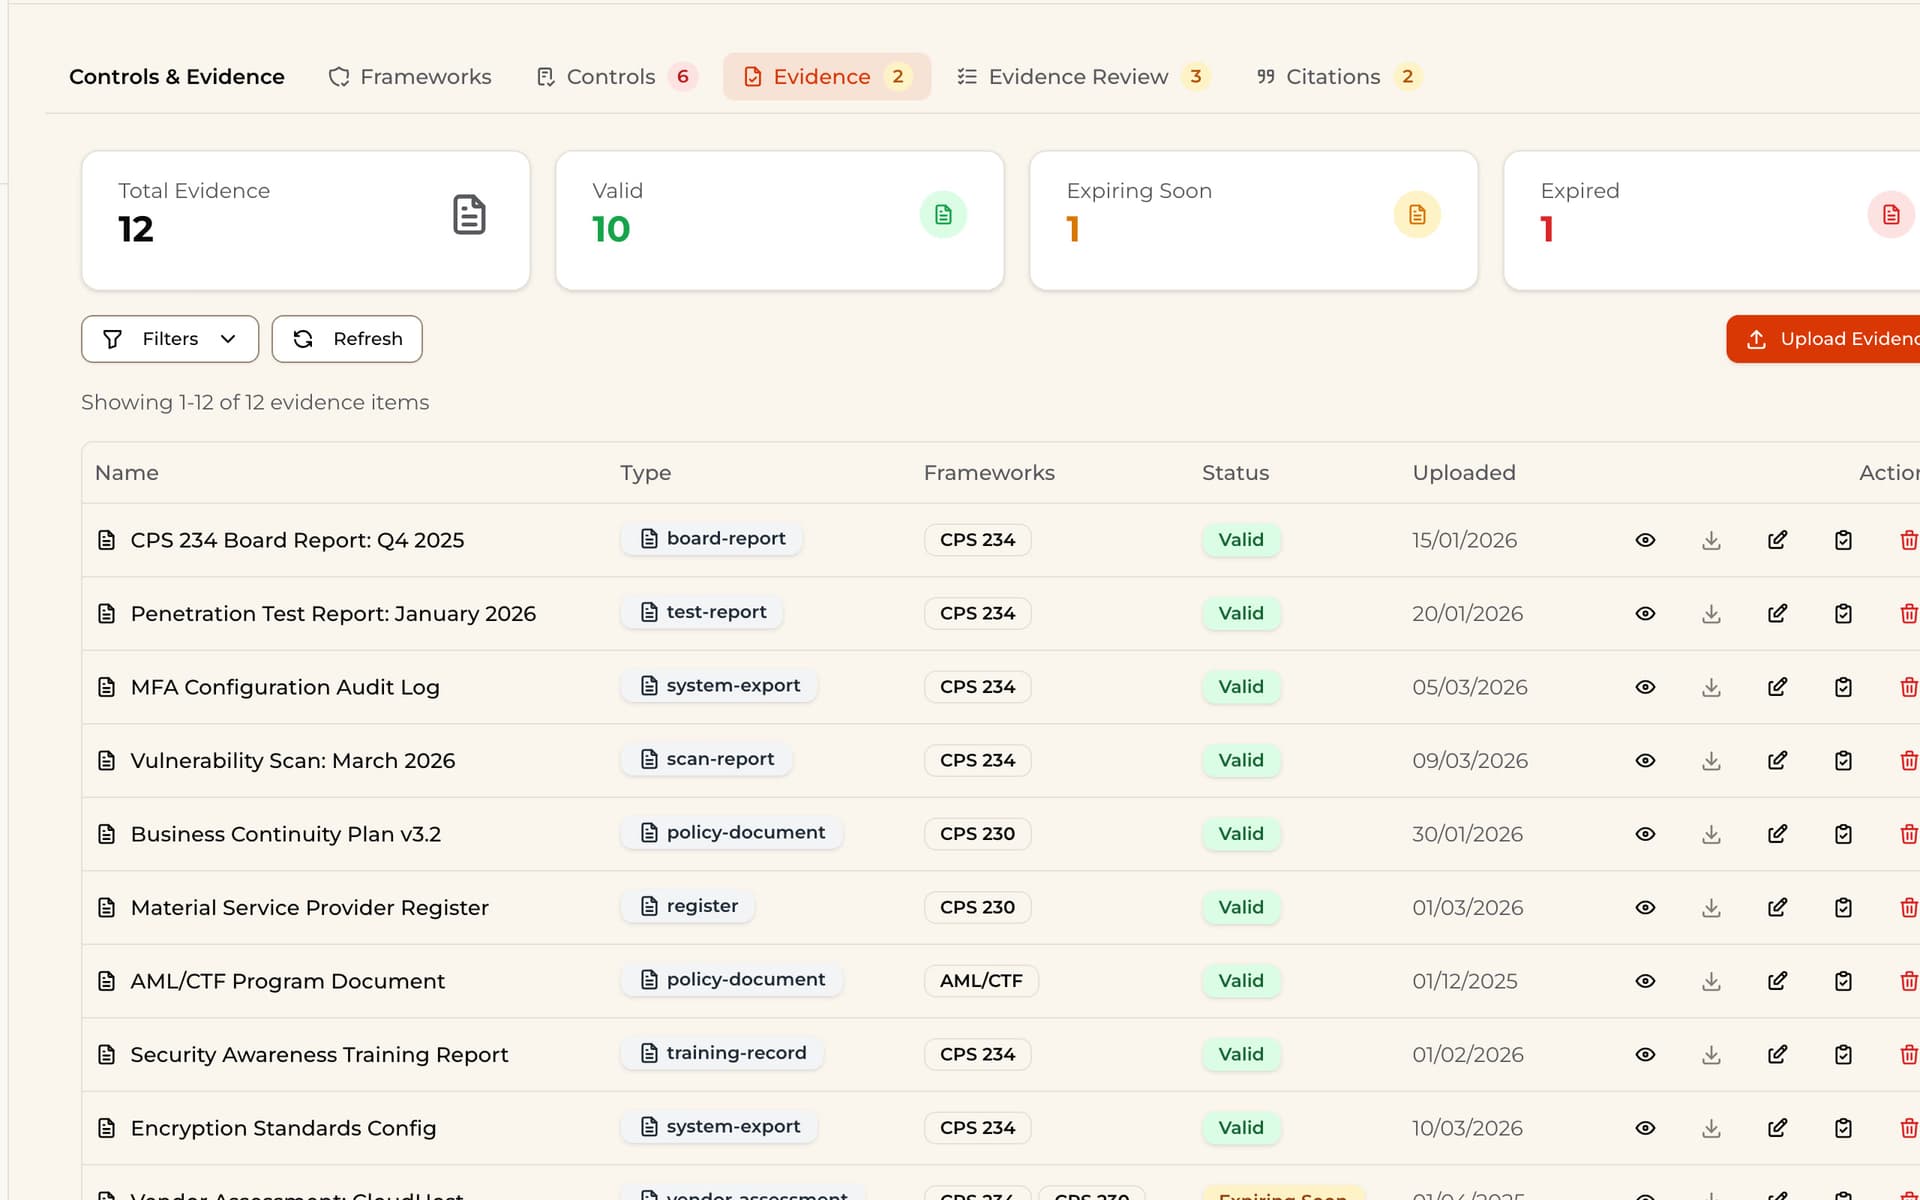
Board reports, test results, policies and scans, each tagged to the frameworks it supports, with its status.
- 02
Let the agents watch
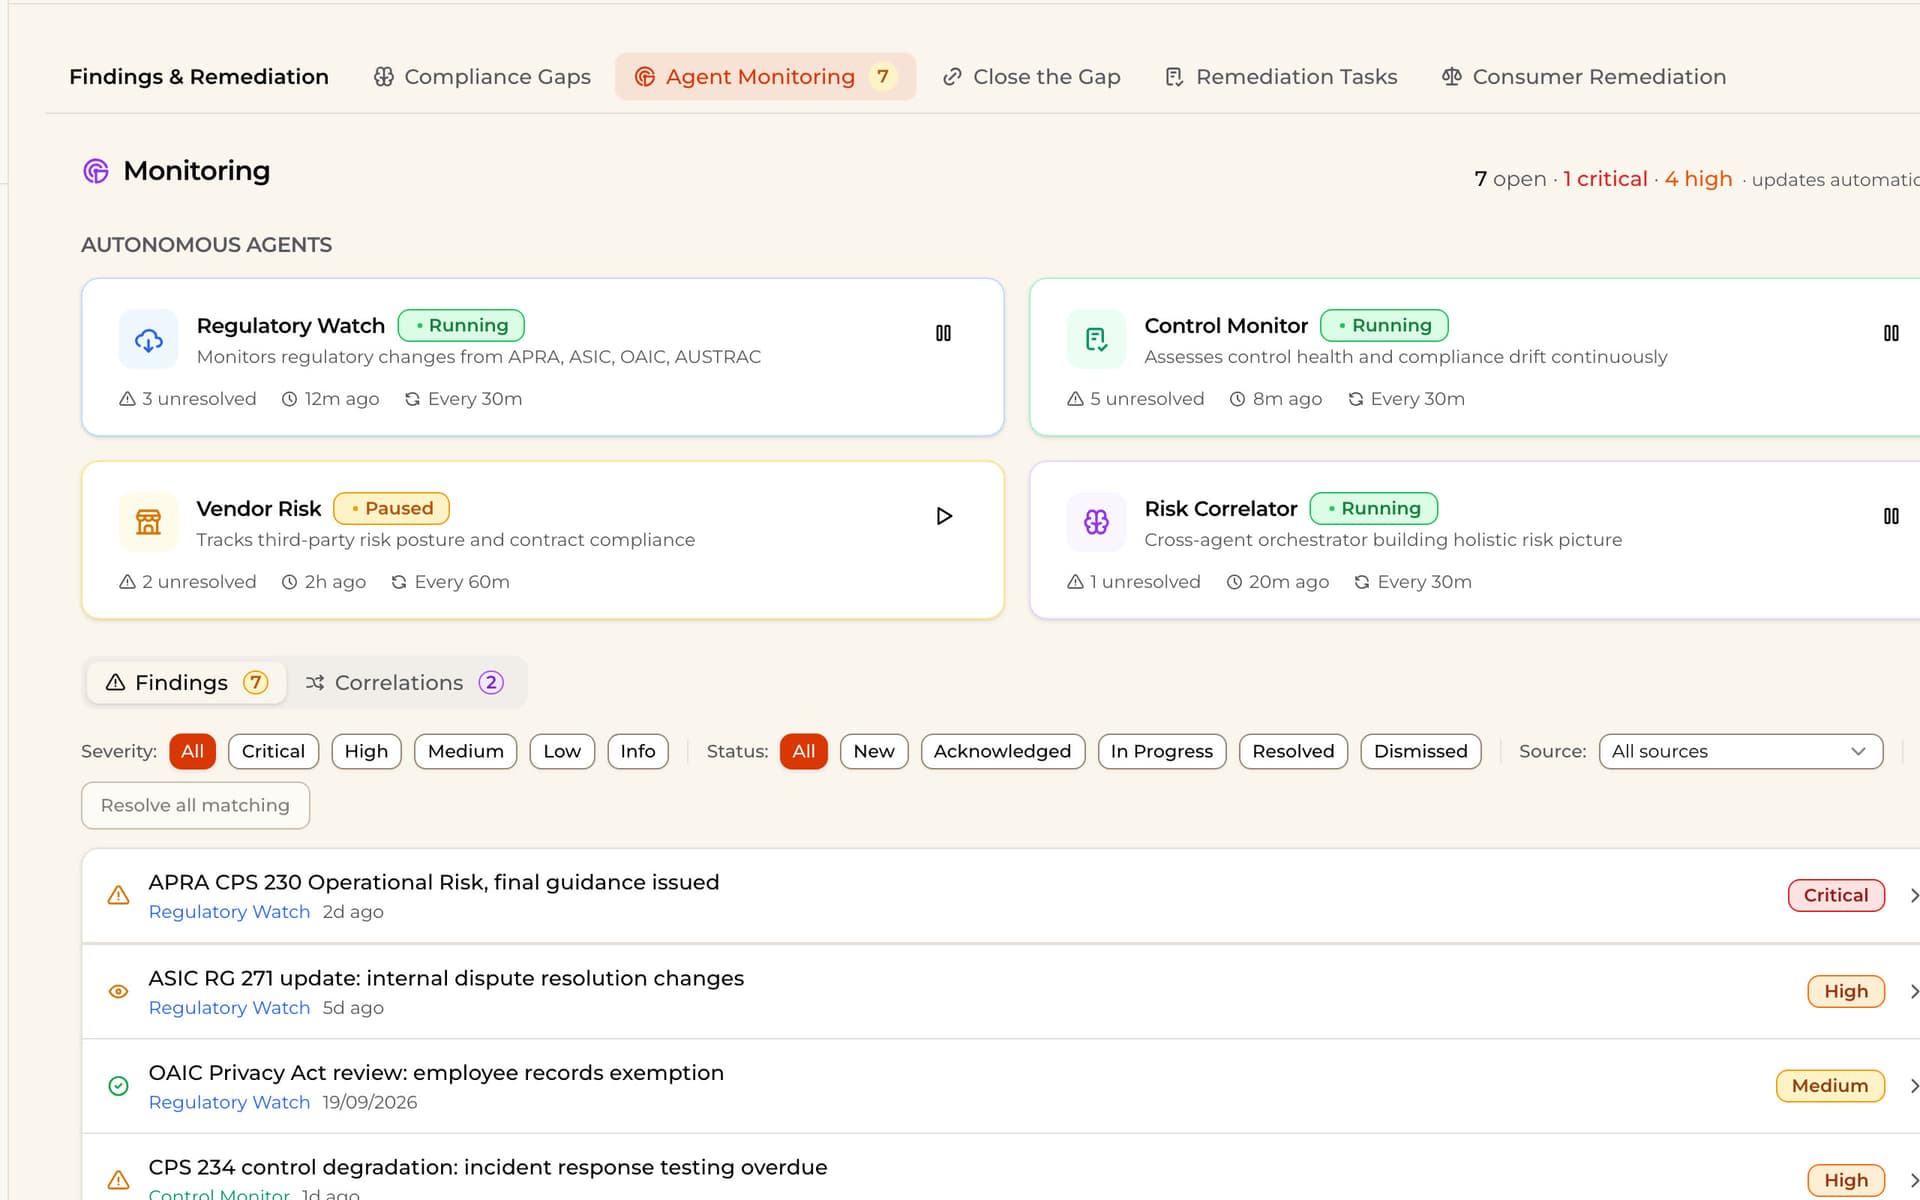
Regulatory Watch, Control Monitor, Vendor Risk and Risk Correlator run continuously and raise findings by severity.
- 03
Test the controls
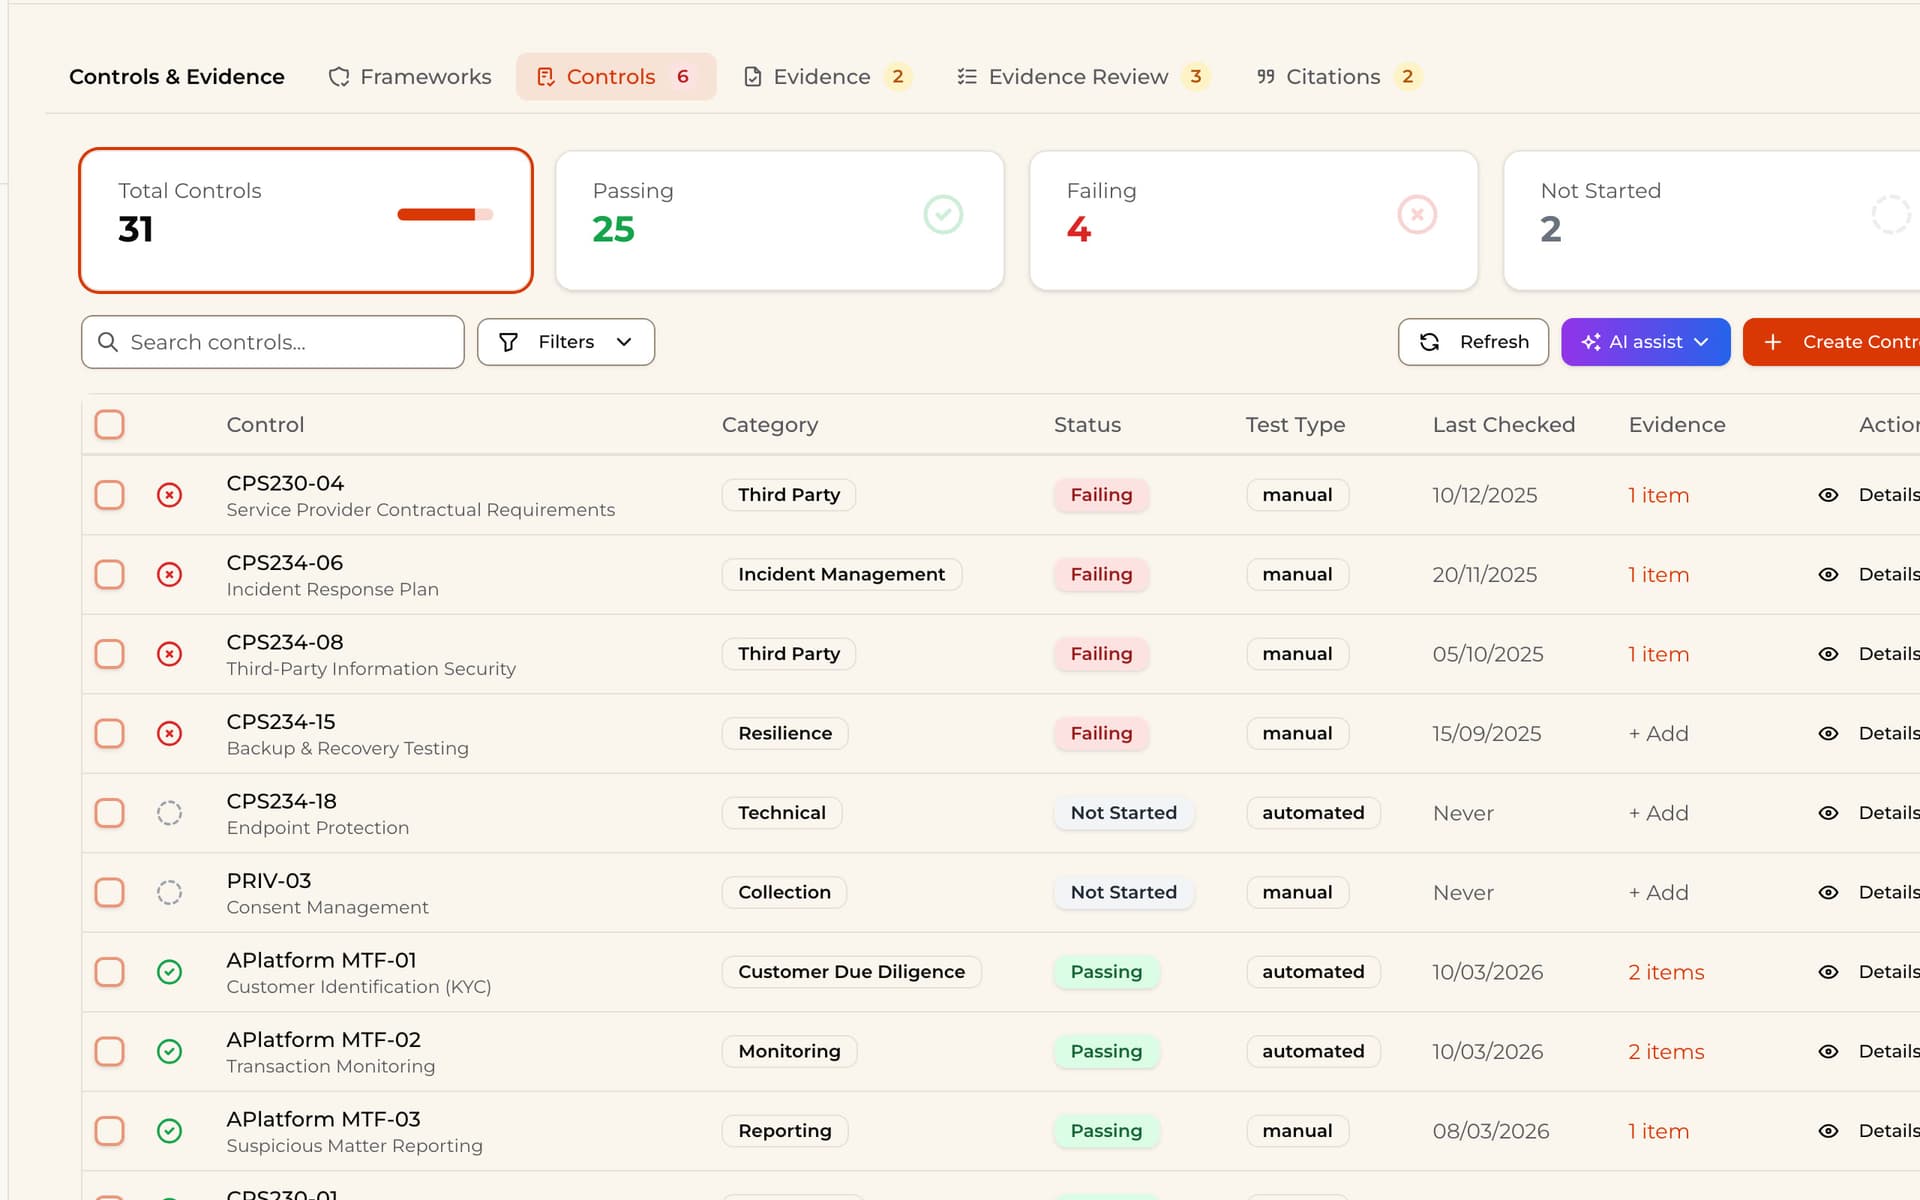
Every control shows whether it is passing, how it is tested, when it was last checked and the evidence behind it.
Audit prep was a project. Now it is a state.
What's included.
Evidence register
Every artefact, its frameworks, status and expiry.
Controls testing
Manual and automated tests, with results and evidence.
Monitoring agents
Regulatory, control, vendor and risk agents, running continuously.
Compliance posture
One score across controls, evidence, gaps and the audit chain.
Audit log
Who changed what, and when, tamper-evident.
Report library
Board and audit reports generated from live records.
“Finally, AI our compliance team actually approves. Everything stays on our servers, audit trails are built in, and our advisers are spending time with clients instead of fighting Word templates.”
 Head of ComplianceFrazer Walker · AFSL holder
Common questions.
What is continuous audit evidence?
Instead of collecting evidence the week before an audit, every policy, test result and attestation is registered against the controls and frameworks it proves as it is created, with its expiry watched.
Which frameworks does BackPro track evidence against?
The frameworks configured for your firm, including CPS 230, CPS 234, APP 11, AML/CTF and RG 271. BackPro holds neither SOC 2 nor ISO 27001 certification.
Does BackPro replace our auditor?
No. It keeps the evidence and the audit trail as you go, so an audit draws on records that already exist.
What do the monitoring agents do?
Regulatory Watch, Control Monitor, Vendor Risk and Risk Correlator run continuously and raise findings by severity for your team to review.
The rest of the platform
- DDQ EngineEvery DDQ, answered from your own documents.Explore
- SoA AutomationAn adviser-ready SoA in about ten minutes.Explore
- Compliance MappingEvery control, mapped to what it answers.Explore
- Knowledge GraphSee how everything connects.Explore
- Compliance SuiteIncidents, breaches and complaints.Explore
See your evidence in one place.
Thirty minutes on video. We walk you through evidence, controls and monitoring the way your compliance team would use them.